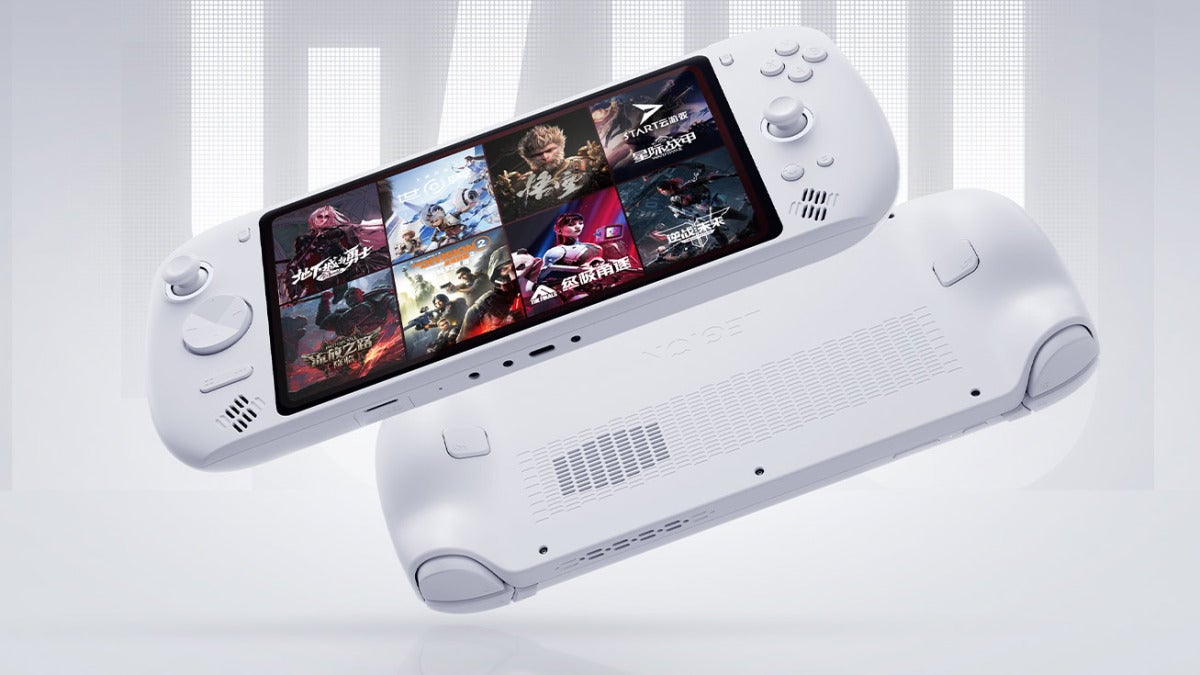
Lenovo Legion C700 launches in China: Android handheld for PC streaming

Lenovo has launched the Legion Cloud Gaming Handheld C700 in China. It’s an Android handheld aimed first at cloud gaming and remote play, and it arrives with Lenovo’s new Legion Stream feature for streaming games from a PC.
Steam Link Download

Specs are pretty straightforward: a MediaTek Dimensity 7400, either 6 GB or 8 GB of RAM, a 7.82-inch Full HD 120 Hz LCD, and an 8,000 mAh battery that Lenovo says can handle up to nine hours of streaming. You also get Hall effect triggers, active cooling, and a body weight of 556 g. The 8 GB/256 GB version sells for 2,199 yuan, or about $327, which puts it much closer to something like the Logitech G Cloud than to the pricier Windows handheld crowd.

What really sets it apart is the bundled dongle. Lenovo says it can stream PC games with a one-touch setup, even without a standard network connection. The company is also claiming sub-10 ms latency in lab testing. Still, there’s not much independent testing yet on latency, stability, the software, battery efficiency, or how well the Tencent START integration and the China-focused software stack would hold up outside China.

If remote play and cloud services are what you mostly use, this looks like a pretty compelling pick over a heavier Windows handheld. If native Android gaming or emulation matters more to you, though, another Android device may make more sense.

Right now, the Lenovo Legion Cloud Gaming Handheld C700 is only available in China, and Lenovo still hasn’t said anything about a global launch.
GitHub goes offline worldwide: nearly eight hours of disruption

GitHub went down worldwide on August 17, 2026, taking out tools many teams depend on for development and day-to-day business workflows for almost eight hours. GitHub said the outage hit the GitHub web interface, the GitHub API, GitHub Actions, GitHub webhooks, pull requests, GitHub Copilot, and enterprise identity features.

GitHub Desktop Download

The company said the incident started at 13:40 UTC and wasn’t fully resolved until 21:15 UTC. At the worst point, GitHub reported roughly a 20% error rate across web and API traffic, while archive downloads and raw content requests were failing at about 50%. For your team, that translated into trouble across the web interface, API requests, Actions, webhooks, pull requests, Copilot, and enterprise identity features such as SAML, OIDC, SCIM, and Team Sync. The result was shaky code access, stalled pipelines, blocked deployments, and sign-ins that simply failed.

GitHub and Microsoft said engineers were investigating as the failures spread and put corrective measures in place to bring services back. Customers are still likely to want a much fuller post-incident account: what actually broke, why so many systems went down at the same time, and what protections will be added to keep it from happening again.

If GitHub is part of your daily routine, this outage lands a little harder. GitHub’s status history reportedly showed eight degradation events in July alone, during a period of heavier automated development, GitHub’s Azure migration, estimates that commit volume is rising from 2025 to 2026, and GitHub’s own plan to expand capacity by 30x. If you want to keep an eye on service availability, GitHub’s status page is the place to check.

Amazon Prime Air sparks scrutiny: drone drops package into pool

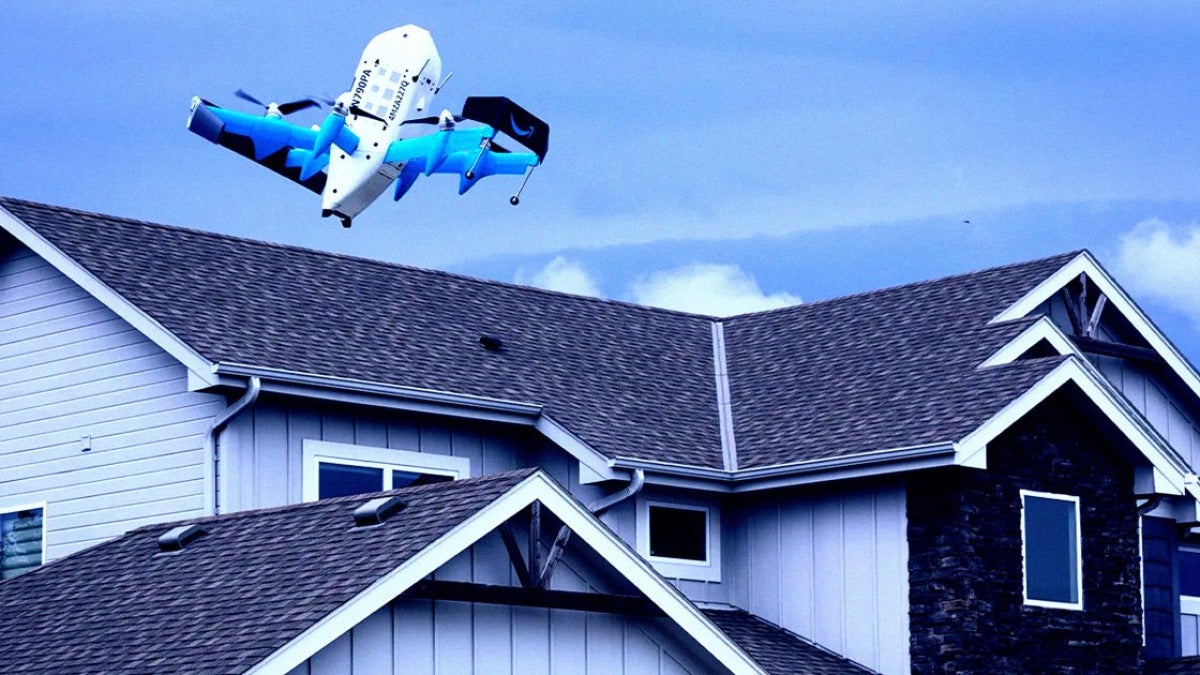
Amazon Prime Air, the company’s drone-delivery arm, got some unwelcome attention this week after one of its drones dropped a package into a customer’s swimming pool in Richmond, Texas. The parcel, visibly soaked, ended up on video.

The timing wasn’t great. In the same week, Amazon said it wants nearly 500 US cities and towns by the end of 2026, roughly six times its current footprint. Amazon says the service is meant for packages up to five pounds delivered in under an hour, which is why a miss into someone’s backyard pool raises obvious questions about reliability.

Amazon called the pool drop “extremely rare,” said its drones use sense-and-avoid technology, and the aircraft involved was likely the MK30. Amazon says that model is lighter, smaller, quieter, and able to fly in a wider range of weather.

If you’re watching drone delivery closely, the bigger story is what this says about Amazon’s position. The company is pushing further into a tougher race with Walmart and Alphabet’s Wing drone-delivery business over sub-hour delivery, and sometimes delivery in under 30 minutes, for household essentials and last-minute purchases.

And this incident doesn’t land in isolation. There were earlier crashes and collisions with a crane and a communications cable, scrutiny from the Federal Aviation Administration and UK authorities, and ongoing arguments over noise, privacy, safety, hacking, local rules, crowded airspace, and the economics of the whole thing. Prime Air is still limited to select areas even though Amazon says it has made hundreds of thousands of deliveries this year, and rare mistakes are always going to draw outsized scrutiny.

Pixel 11 factory images are now available for all four models

Google just posted factory images for the full Pixel 11 family: the Pixel 11, Pixel 11 Pro, Pixel 11 Pro XL, and Pixel 11 Pro Fold. That means manual recovery and flashing downloads are now live through Google’s developer channels. Official Android 17 images are available for all four phones, with three builds listed for each model. In Google’s listings, the codenames are cubs, grizzly, kodiak, and yogi.

These aren’t the usual over-the-air updates. They’re the complete stock software packages you’d use to restore a phone, roll back from a bad test build, recover from a failed update, or do a clean install from scratch. You do need to choose carefully , because the image has to match your device exactly, including the right regional, carrier, or certification build. Timing matters here too. These factory images are showing up right as Google ramps up its wider Pixel 11 push, centered on the DeepMind-influenced Tensor G6 and tighter Gemini integration through features like Proactive Intelligence and Rambler. At the same time, some developers are uneasy about Google making kernel source access available on request, since that could slow down custom ROM work.

If you manually flash stock software or build for Pixel, this is the kind of release you’ll want on hand. The factory images are up now in Google’s developer channels.

Vivodyne unveils the world’s largest biological datacenter

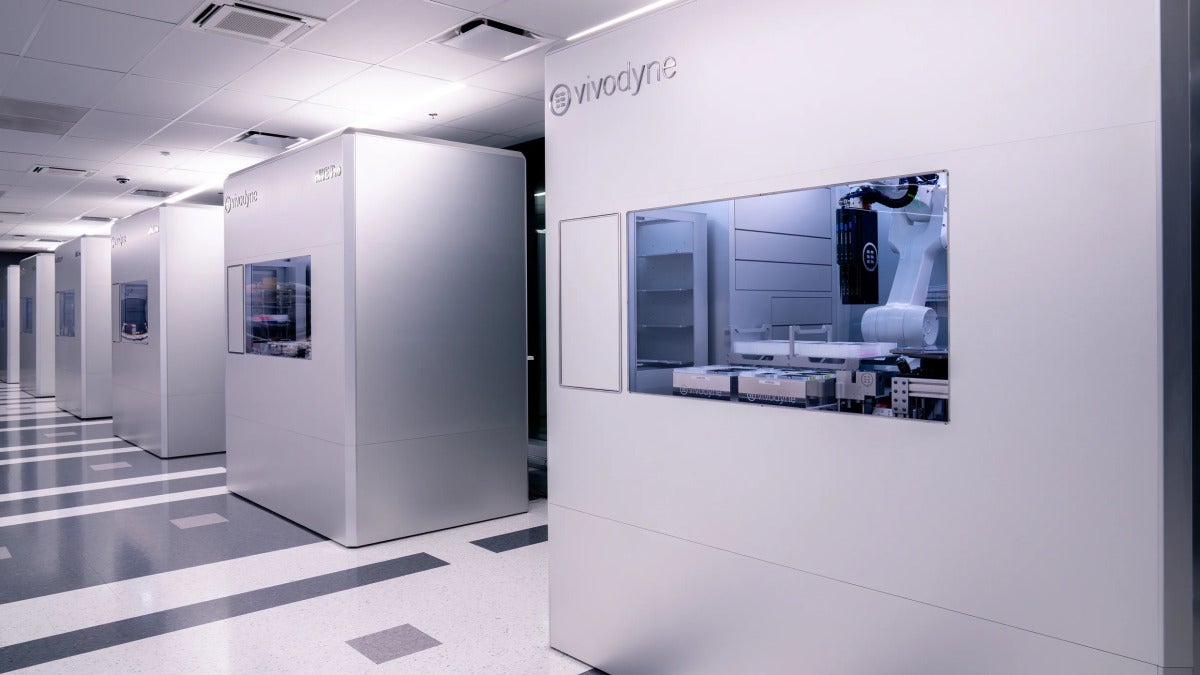
California startup Vivodyne said today that it has built what it calls the world’s largest biological datacenter, a robotic drug-testing setup that screens medicines on lab-grown human tissue rather than leaning so heavily on mice and dogs.

The company says the platform brings together software, robotics, and more than 20 tissue types, including liver, lung, and bone marrow, across 12 HIVE labs. The idea is to test safety and efficacy at a scale of about 3.1 million tissues per year, which Vivodyne says is roughly twice the scale of all U.S. clinical trials combined.

Vivodyne’s argument is straightforward: 90% to 95% of drugs that look successful in animal tests still fail in humans. If those failures can be spotted earlier with human tissue models, that could improve the pool of drugs that make it into human trials. The push also lines up with broader moves across the industry, including work from Emulate, CN Bio, and Hesperos, along with backing from the U.S. Food and Drug Administration after the 2022 Modernization Act 2.0.

If you track drug development, this is a platform to keep an eye on. It still doesn’t replace animal testing outright, though, because drug developers need whole-body biology too, including immune interactions, blood flow, and system-wide drug effects.

Vivodyne also says it has raised $79.6 million, including a $40 million Series A led by Khosla Ventures in May 2025, and that its expanded work will operate out of a new 23,000-square-foot lab in South San Francisco.

Apple reportedly tests Chinese memory chips for future iPhones and MacBooks

Apple is said to be testing memory chips from ChangXin Memory Technologies, or CXMT, China’s biggest DRAM maker, for future iPhones and MacBooks. If it moves forward, that would mark a real change from Apple’s usual dependence on Samsung, SK Hynix, and Micron.

People familiar with the matter say Apple is evaluating CXMT’s DRAM at a moment when the memory market is getting tighter. Apple has good reason to want another qualified supplier: less exposure if one vendor slips, and a stronger hand on both price and volume for a core component used across its products.

That pressure comes from the wider memory squeeze. Strong data-center demand for high-bandwidth memory is tightening supply and lifting prices for conventional memory along with it, so testing CXMT gives Apple a fallback if its current suppliers keep prioritizing more lucrative product lines or if pricing gets worse.

If you follow Apple’s hardware supply chain, this is one to watch. Politics could still put limits on it, though. Any Apple-CXMT arrangement would almost certainly draw US scrutiny, which makes standard off-the-shelf memory far more likely than deeply customized chips.

So don’t expect to see CXMT memory in the next iPhone 18 Pro. That product is already deep in development, CXMT’s production lines are said to be booked for the rest of the year, and its pricing may end up similar to, or even higher than, what Samsung and SK Hynix are charging.

There’s nothing for you to download here yet. Still, after CXMT’s July 2026 IPO and its push into LPDDR6, Apple’s testing looks a lot like a hedge on future supply flexibility.

DOGE audit is out: watchdog says savings claims were inflated

The U.S. Government Accountability Office released an audit today on the Department of Government Efficiency, or DOGE, and its conclusion was blunt: the federal cost-cutting push overstated how much money it saved.

DOGE started out with a $2 trillion goal. Later, it put a $215 billion figure on its public “Wall of Receipts.” But when the Government Accountability Office reviewed about $110 billion of those claimed savings, it found that a large share of them couldn’t be verified, relied on faulty math, or came from actions that were already underway before DOGE even existed.

Some of the examples are hard to brush off. The Government Accountability Office said $27.4 billion came from contracts that were never actually terminated. The audit also found that nearly 2,000 of the 13,476 contracts DOGE claimed it had ended were still active. One Defense Health Agency IT contract, tied to $1.7 billion in claimed savings, was never terminated or modified at all, according to the audit. The Government Accountability Office also said 96% of the reported grant savings couldn’t be verified, and that 108 lease cancellations had already been set in motion before DOGE was created.

The audit was requested by U.S. Senators Gary Peters and Richard Blumenthal. They said DOGE had been deceptive and reckless. Outside policy and procurement experts were just as skeptical, describing it as startup-style behavior dropped into a system built around contracting rules, legal requirements, and long government timelines. Some said it looked less like real budget cutting and more like performance art.

If you followed DOGE through the viral claims and flashy receipt pages, this Government Accountability Office report changes the picture. You can read the audit on the Government Accountability Office website.

Nvidia says safe, open AI will sell more chips

Nvidia began recruiting today for a new engineering team focused on the security of generative software. The move makes perfect sense: if companies place more trust in these systems, they’ll launch more services—and with that, they’ll need more computing power. That’s exactly where the company excels. The job postings reveal that this group will focus on security and protection, and this is no small team: among the positions being sought is even a “technical leader for the founding team.”

According to those same job postings, the work will include validating agents before deploying them to production and creating tools capable of detecting and correcting software vulnerabilities. The idea is to strengthen these systems before they enter real-world environments.

The initiative is part of a broader strategy by Nvidia.

The company has long been an advocate of open models. Its argument is that transparency and public scrutiny help strengthen both security and technological competitiveness. Jensen Huang, Nvidia’s CEO, has publicly defended this stance and maintains that it improves cybersecurity and reduces risks by allowing more researchers and developers to examine how the systems work.

And this is no minor matter for Nvidia.

Meta launches Muse Code: coding agent now on macOS and Linux

Meta has released Meta Muse Code, a terminal-based coding assistant for macOS and Linux, and it’s clearly built for people working in real codebases, not toy projects.

Visual Studio Code Download

The company says you can install Meta Muse Code with a single command. From there, it’s meant to handle the full loop across large repositories: planning code changes, writing the code, and checking the results. Meta is also leaning on persistent background agents, plus an event log that lets you pick back up after a crash or any other interruption.

On pricing, Meta says the standard tier starts at $1.25 per million input tokens and $4.25 per million output tokens. There’s also a contributor tier that drops those rates to $0.10 and $0.20, but only if you agree to let Meta use your prompts and code for future training. That puts Meta Muse Code in direct competition with OpenAI Codex, Anthropic Claude Code, and GitHub Copilot, not just on performance, but on price too.

If you’re after a lower-cost coding assistant, this is probably an update worth trying. If your day-to-day work involves proprietary code, though, that tradeoff may be a lot harder to swallow.

The release lands in the middle of a broader rush around coding tools. Forecasts for the market are all over the place, from $4.2 billion in 2025 to somewhere between $6.9 billion and $40.7 billion by the mid-2030s. Meanwhile, 84% of developers already use these tools or expect to, while only 29% fully trust the code they generate. That gap matters, especially as Meta looks for new revenue beyond Llama. Meta Muse Code is available now on macOS and Linux.