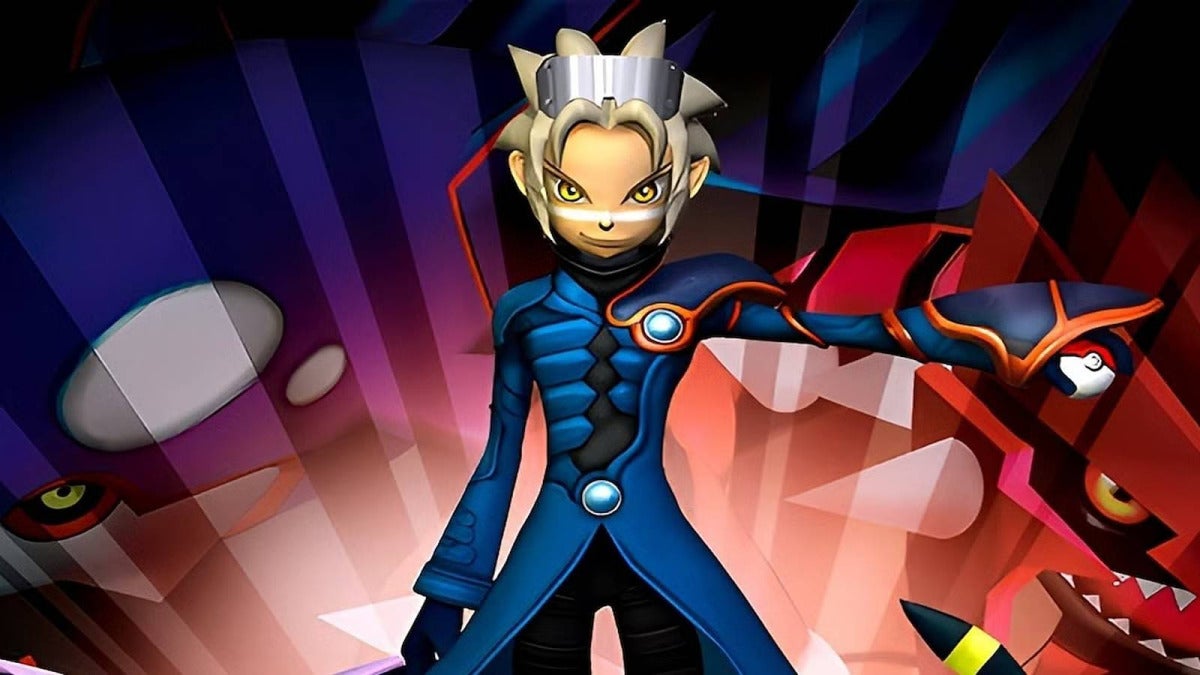
Nintendo has finally confirmed that Pokémon Colosseum, the GameCube spin-off, is headed to Nintendo Switch 2 through the GameCube Classics library on Nintendo Switch Online. What it hasn’t done is give the game a release date.
It’s been more than a year since Nintendo first included Pokémon Colosseum in its Nintendo Switch 2 retro plans, and all the company has said since then is that the game is still on the way. No reason for the hold-up, no real update. It’s easy to see why fans are annoyed, especially when Pokémon XD: Gale of Darkness made it in first.
If you’ve been hoping to replay that stretch of the series in order, Colosseum is still one to watch. It remains one of the strangest, most memorable Pokémon spin-offs Nintendo has ever put out.
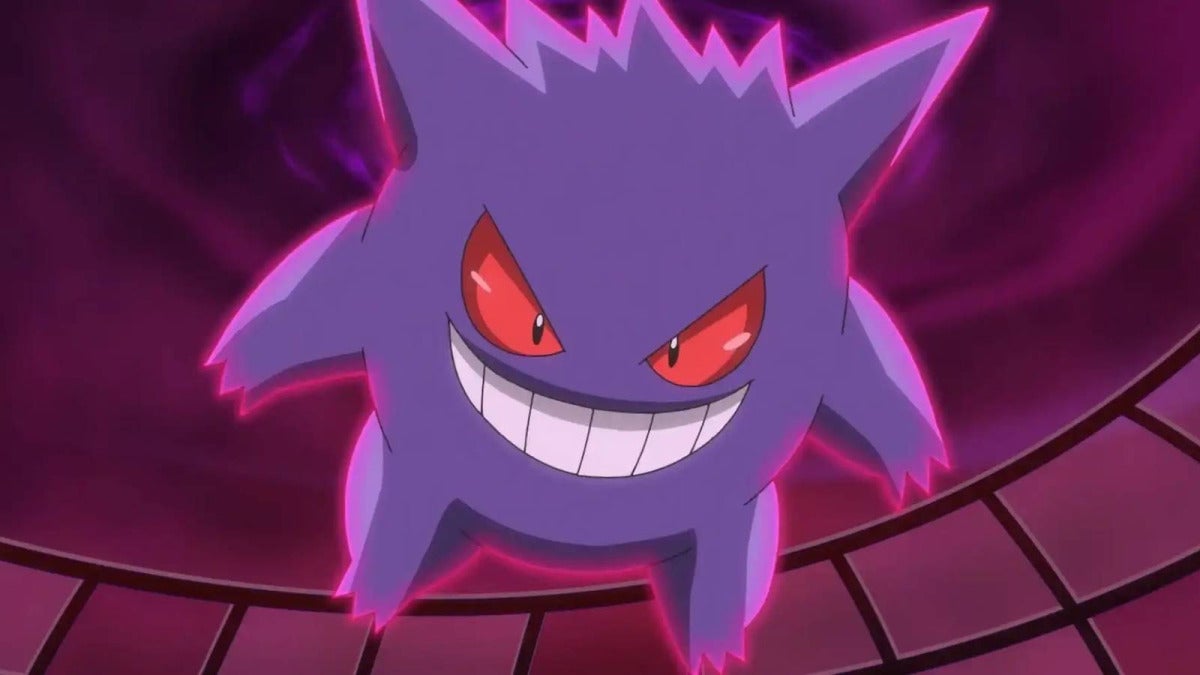
Colosseum took players to the Orre region and centered the whole thing on Shadow Pokémon. It leaned into “snagging,” a darker story than the mainline games usually go for, and double battles as a core part of how you played. That’s why people have been asking for a modern rerelease for years.
For now, all anyone has are fan theories. Maybe Nintendo is figuring out Pokémon HOME support. Maybe there are technical issues tied to saves and save states. Meanwhile, the GameCube rollout keeps moving, with new additions showing up every one to three months.
When it does arrive, Pokémon Colosseum will be available through Nintendo Switch Online on Nintendo Switch 2. Right now, the GameCube lineup includes Fire Emblem: Path of Radiance, Mario Smash Football, Pokémon XD: Gale of Darkness, and The Legend of Zelda: The Wind Waker.