Skip to content

Softonic English

Just another Softonic Sites site

Tag: Seguridad

Temas

If you have experienced failures trying to connect to your favorite gaming platforms, it's not you: they have suffered a massive DDoS attack

A sudden increase in failure reports from platforms like Steam, Xbox, PlayStation, Riot Games, and Epic has sparked speculation about a possible massive DDoS attack. Downdetector’s records indicate that this spike in connectivity issues occurred around 11 PM ET on October 6, which has led analysts to link these incidents as part of the same phenomenon. Riot and Steam have been hit the hardest. Riot Games, in particular, has confirmed that it has been facing intermittent network issues that have affected its popular […]

If you have experienced failures trying to connect to your favorite gaming platforms, it's not you: they have suffered a massive DDoS attack

A sudden increase in failure reports from platforms like Steam, Xbox, PlayStation, Riot Games, and Epic has sparked speculation about a possible massive DDoS attack. Downdetector’s records indicate that this spike in connectivity issues coincidentally occurred around 11 PM ET on October 6, leading analysts to link these incidents as part of the same phenomenon.

Riot and Steam have taken the worst part

Riot Games, in particular, has confirmed that it has been facing intermittent network issues that have affected its popular game League of Legends and its shooter Valorant. In a statement, Riot spokesperson Joe Hixson mentioned that their team has been working to resolve these issues and that proactive measures have been taken to protect the player experience, including the temporary disabling of ranked queues in some regions and the implementation of compensations for lost rank points.

Speculations suggest that the attack may have been launched through the Airsuru botnet, known for carrying out large-scale DDoS attacks. According to a report from Cloudflare, the Airsuru botnet has conducted attacks that are twice as volumetric as anything previously seen on the network, highlighting the seriousness of the current situation.

While the nature of the attack has not yet been officially confirmed, the coincidence and magnitude of the problems have fueled the theory that it could be a show of power by the perpetrators. Some users on platforms like Reddit suggest that this apparent display may be intended to demonstrate the ability to affect even targets that are traditionally considered resilient to such incidents.
Steam
Steam DOWNLOAD
Author SoftonicPosted on October 9, 2025October 9, 2025Categories Gaming, NewsTags Airsuru, ciberseguridad, DDoS masivo, Epic, Playstation, Reddit, Seguridad, Steam

Discord confirms that its users' data has been compromised

Discord, the popular communication platform among gamers, has confirmed that a third-party customer service provider has been compromised, allowing attackers to access user data. This incident represents a significant risk to the privacy and security of the personal information of the platform’s users. Your data may not be safe According to the company, the attackers not only managed to access sensitive information but also intend to extort a sum of money in exchange for not disclosing the obtained data. This type of attack highlights the vulnerabilities […]

Discord confirms that its users' data has been compromised

Discord, the popular communication platform among gamers, has confirmed that a third-party customer service provider has been compromised, allowing attackers to access user data. This incident poses a significant risk to the privacy and security of the personal information of the platform’s users.

Your data may not be secure

According to the company, the attackers not only managed to access sensitive information but also intend to extort a sum of money in exchange for not disclosing the obtained data. This type of attack highlights the vulnerabilities that may exist in the supply chains of technology companies, as they often rely on third parties to manage critical information.

The implications of this attack are concerning, given that Discord has millions of users who use the platform to communicate, play, and share content online. The nature of the unauthorized access to data raises serious doubts about the company’s ability to protect its users’ information. It is essential for platforms of this kind to implement more robust security measures, given the increasing number of cyberattacks in the industry.

Discord has begun an internal investigation to assess the extent of the impact and is working to notify affected users. Additionally, the company has urged all its users to be vigilant for any suspicious activity that may arise as a result of this incident. Over the years, data security attacks have increased, and organizations must proactively adapt to mitigate these risks.

This attack also reflects a broader trend in the digital world, where criminals are increasingly willing to threaten users’ personal security in order to gain financial benefits. In this context, strengthening cybersecurity measures becomes more crucial than ever.

Discord
Discord DOWNLOAD
Author SoftonicPosted on October 9, 2025October 9, 2025Categories GuidesTags ataque, brecha de seguridad, ciberseguridad, discord, información sensible, Seguridad

Gemini could have critical vulnerabilities that make its use dangerous

Researchers from Tenable, a renowned cybersecurity company, have discovered three vulnerabilities in Gemini, the artificial intelligence tool developed by Google. This finding raises concerns among security experts, as Gemini is used in various applications that could be affected by these flaws. The revelation underscores the importance of security in the field of artificial intelligence, a sector that continues to grow and evolve rapidly. If you use Gemini, you could be putting your system at risk. The vulnerabilities identified in Gemini could allow an attacker to compromise the integrity of the system, accessing sensitive information or even taking control of […]

Gemini could have critical vulnerabilities that make its use dangerous

Researchers from Tenable, a renowned cybersecurity company, have discovered three vulnerabilities in Gemini, the artificial intelligence tool developed by Google. This finding raises concerns among security experts, as Gemini is used in various applications that could be affected by these flaws. The revelation underscores the importance of security in the field of artificial intelligence, a sector that continues to grow and evolve rapidly.

If you use Gemini, you could be putting your system at risk

The vulnerabilities identified in Gemini could allow an attacker to compromise the integrity of the system, gaining access to sensitive information or even taking control of applications dependent on this technology. Although the specific details about the vulnerabilities have not yet been fully disclosed, Tenable has indicated that they have taken steps to notify Google, which is currently assessing the related risks and working on possible solutions.

Gemini, as an artificial intelligence tool, is used in a wide range of applications, from chatbots to business automation processes. The versatility of this tool makes it an attractive target for malicious agents. With the growth of artificial intelligence, companies face increasingly greater challenges regarding the security of their systems.

Google is no stranger to security issues, having previously dealt with similar situations in other products. Timely responses to these vulnerabilities are crucial to maintaining user trust and safeguarding the technology that companies are increasingly beginning to rely on. Industry observers suggest that such incidents should serve as a wake-up call about the need to strengthen security measures in artificial intelligence tools.

Gemini
Gemini DOWNLOAD
Author SoftonicPosted on October 2, 2025October 2, 2025Categories News, Software>SecurityTags chatbots, ciberseguridad, Gemini, Google, IA, inteligencia artificial, Seguridad, Tenable

8,424 cryptocurrency wallets are stolen due to a cybersecurity issue

Cybersecurity researchers have discovered two malicious crates in Rust that masquerade as a legitimate library called fast_log, in order to steal Solana and Ethereum wallet keys from the source code. The crates, named faster_log and async_println, were published by a threat actor under the pseudonyms rustguruman and dumbnbased on May 25, 2025, achieving a total of 8,424 downloads, according to the software supply chain security company, Socket. Make sure you know what you are downloading These fraudulent crates include functional logging code as a cover and contain routines […]

8,424 cryptocurrency wallets are stolen due to a cybersecurity issue

Cybersecurity researchers have discovered two malicious crates in Rust that impersonate a legitimate library called fast_log, in order to steal Solana and Ethereum wallet keys from the source code. The crates, named faster_log and async_println, were published by a threat actor under the pseudonyms rustguruman and dumbnbased on May 25, 2025, achieving a total of 8,424 downloads, according to the software supply chain security company, Socket.

Make sure you know what you are downloading

These fraudulent crates include functional registration code as a cover and contain routines that scan source files for private keys of Solana and Ethereum. Once identified, they exfiltrate the matches through an HTTP POST request to a hardcoded command and control (C2) endpoint, according to security researcher Kirill Boychenko.

Following the responsible disclosure of the finding, the maintainers of crates.io have taken steps to remove the Rust packages and disable the two involved accounts. In addition, they have preserved the records of the users operated by the threat actor along with the malicious crates for further analysis. “The malicious code was executed at runtime, when running or testing a project that depended on them,” commented Walter Pearce from crates.io.

In a typosquatting attack, the actors maintained the original library’s registration functionality while introducing malicious changes during a packaging operation, which recursively searched for Rust files in a directory to find private keys. This attack is a clear reminder of how minimal code and a simple deception can create a significant risk in the supply chain, allowing malicious code to reach developers’ computers and continuous integration systems.

Avast Free Antivirus
Avast Free Antivirus DOWNLOAD
Author SoftonicPosted on September 26, 2025September 26, 2025Categories NewsTags ciberseguridad, crates, criptomonedas, fast_log, privacidad, Rust, Seguridad, typosquatting

If your company has hired a spy from North Korea, this is what you should do according to cybersecurity experts

Companies face significant legal and financial risks when discovering that they have inadvertently hired information technology (IT) workers from North Korea. These incidents can reveal an organized employment scheme that generates income for the North Korean regime’s weapons programs, further complicating the situation for the affected organizations. First of all, try by all means not to hire North Korean spies. Cybersecurity experts warn that, although North Korean workers may be linked to weapons programs, their main motivation is to earn a salary. This changes the dynamic of how the […]

If your company has hired a spy from North Korea, this is what you should do according to cybersecurity experts

Companies face significant legal and financial risks when discovering that they have inadvertently hired information technology (IT) workers from North Korea. These incidents can reveal an organized employment scheme that generates revenue for the North Korean regime’s weapons programs, further complicating the situation for the affected organizations.

First of all, try by all means not to hire North Korean spies

Cybersecurity experts warn that, although North Korean workers may be linked to weapons programs, their main motivation is to earn a salary. This changes the dynamic of how companies should handle these situations. Attendees at the Cyber Defense Summit in Washington, D.C., suggest that companies should collaborate among their human resources, security, and legal departments to identify warning signs during the hiring process.

Among the risk indicators are unvalidated emails, LinkedIn profiles with recycled resumes, and the lack of willingness of candidates to conduct video interviews. Early detection is crucial, as organizations may be exposed to sanction violations even if a payment to a North Korean employee is made inadvertently.

Once a company suspects that it has hired a worker from North Korea, decisions about terminating employment are not straightforward. Experts say it is essential to maintain communication with these employees in order to facilitate the gathering of evidence and the recovery of equipment. Workers tend to be cooperative, interested in recovering their last paycheck before their employment relationship is terminated.

Although there is no legal obligation to notify authorities about these findings, experts emphasize that voluntary disclosure can be beneficial and may reduce penalties in the event of a violation. The threat of these incidents continuing to expand remains, turning this issue into a persistent challenge for companies. These cases indicate that the danger of cybersecurity is far from disappearing.

Avast Free Antivirus
Avast Free Antivirus DOWNLOAD
Author SoftonicPosted on September 24, 2025September 24, 2025Categories News, Software>SecurityTags Corea del Norte, Cyber Defense Summit, empresas, hacker, recursos humanos, RRHH, Seguridad

1 in 3 Android apps have serious API leakage issues, according to a recent study

A recent investigation has revealed that one third of applications on Android and more than half of applications on iOS have serious API leakage issues. These failures can compromise user security and alarmingly expose sensitive data. In a context where the protection of personal information is paramount, these findings raise questions about the responsibility of developers in safeguarding user privacy. The ecosystem is anything but secure The study has highlighted that many of these applications contain encoded secrets of […]

1 in 3 Android apps have serious API leakage issues, according to a recent study

A recent investigation has revealed that one third of applications on Android and more than half of applications on iOS have serious API leakage issues. These flaws can compromise user security and alarmingly expose sensitive data. In a context where the protection of personal information is paramount, these findings raise questions about the responsibility of developers in safeguarding user privacy.

The ecosystem is anything but safe

The study has highlighted that many of these applications contain inadequately encoded secrets, potentially allowing unauthorized access to critical information. This problem not only affects consumers who use these applications to handle sensitive data, but also poses a considerable risk to the developers themselves, who could face legal and reputational repercussions if data breaches occur due to these vulnerabilities.

The leakage of APIs and sensitive information poses a serious risk in an environment where cybersecurity is becoming increasingly crucial. Application platforms must implement stricter regulations to ensure that developers follow best practices in handling sensitive information and coding secrets. Meanwhile, users must be aware of the risks associated with the applications they use and consider the validity of the security measures offered.

Technology companies are under pressure to quickly address these vulnerabilities to protect both their consumers and their own integrity. This growing security issue in mobile applications is an urgent reminder that cybersecurity must be a priority in software development and maintenance. As always, users are advised to keep their devices and applications updated and to stay informed about best security practices.

Android 14
Android 14 DOWNLOAD
Author SoftonicPosted on September 19, 2025September 19, 2025Categories NewsTags Android, API, ciberseguridad, iOS, móvil, Seguridad, smartphone, software, teléfono inteligente

If you have cryptocurrency wallets, a way has been discovered in which they could steal your credentials from them

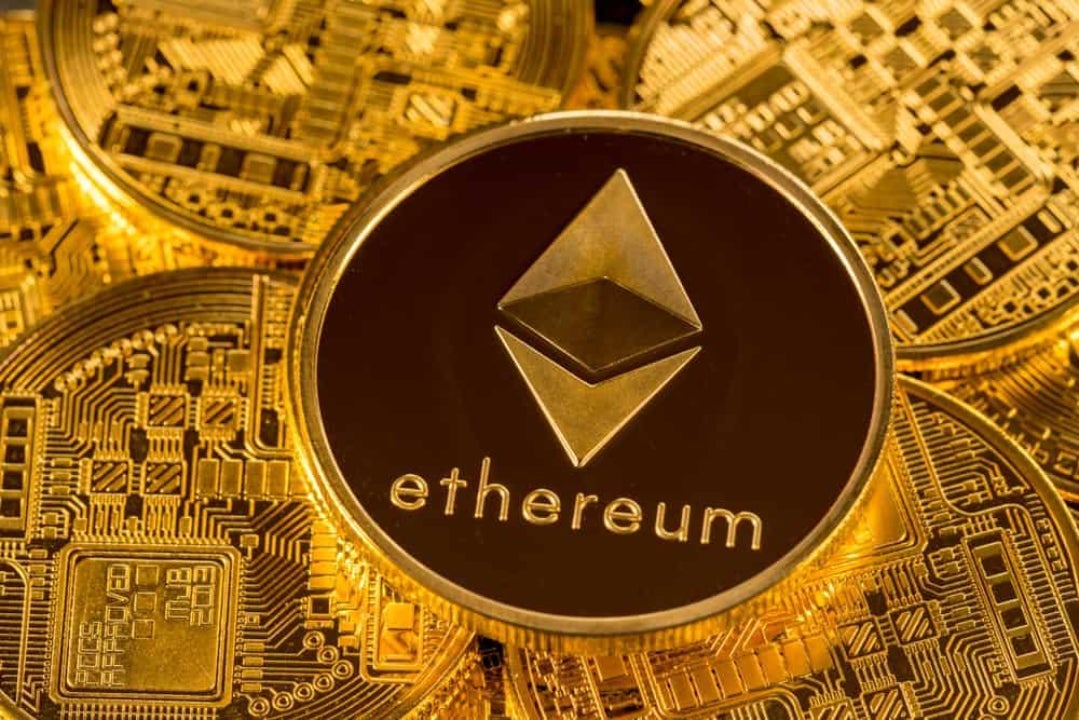
Recently, four malicious packages have been discovered in the npm registry that have the ability to steal cryptocurrency wallet credentials from Ethereum developers. These packages, uploaded by a user calling themselves ‘flashbotts’, masquerade as legitimate cryptographic utilities and the Flashbots infrastructure, while exfiltrating private keys and seed phrases to a Telegram bot controlled by the attackers. A tremendously serious security issue Among the identified packages, ‘ @flashbotts/ethers-provider-bundle’ stands out, designed to hide malicious operations behind seemingly innocuous functions. This package incorporates functionality that redirects unsigned transactions to a […]

If you have cryptocurrency wallets, a way has been discovered in which they could steal your credentials from them

Recently, four malicious packages have been discovered in the npm registry that have the ability to steal cryptocurrency wallet credentials from Ethereum developers. These packages, uploaded by a user calling themselves ‘flashbotts’, impersonate legitimate cryptocurrency utilities and the Flashbots infrastructure, while exfiltrating private keys and seed phrases to a Telegram bot controlled by the attackers.

A tremendously serious security problem

Among the identified packages, ‘@flashbotts/ethers-provider-bundle’ stands out, designed to hide malicious operations behind seemingly innocuous functions. This package incorporates functionality that redirects unsigned transactions to a wallet controlled by the attacker and also captures metadata from pre-signed transactions. Even more alarming, this type of deceptive handling could allow criminals to take full control of the victims’ accounts.

The attacks are designed to exploit the trust placed in Flashbots, an entity widely recognized for its role in mitigating the adverse effects of Maximal Extractable Value (MEV) on the Ethereum network. This context of trust facilitates the inadvertent adoption of these malicious packages by developers seeking legitimate tools for their projects.

Investigations indicate that malicious packages not only operate under the guise of seemingly benign functions, but can also be activated in the code of projects without the knowledge of their developers. The inclusion of comments in Vietnamese in the code suggests that the attackers may be Vietnamese speakers.

According to experts, the existence of these malicious packages turns Web3 development into a direct conduit to bots controlled by criminals, which poses a considerable risk to the security of cryptocurrency investments. The appropriation of private keys in this environment can lead to irreversible theft of funds, raising serious concerns for the Ethereum developer and user community.

Avast Free Antivirus
Avast Free Antivirus DOWNLOAD
Author SoftonicPosted on September 9, 2025September 9, 2025Categories NewsTags billeteras de criptomonedas, ciberseguridad, criptomonedas, ethereum, hackers, Hacking, MEX, red Etherum, Seguridad, Web3

The owner of Burger King and Popeyes suffers a cyberattack that describes its security practices as terrible

Restaurant Brands International (RBI), owner of well-known chains like Burger King, Popeyes, and Tim Hortons, has been the target of a cyber attack that revealed serious vulnerabilities in its IT security. Two hackers, known as BobDaHacker and BobTheShoplifter, published a blog detailing their findings, highlighting their ability to access all RBI locations and listen to conversations in the drive-thrus. In the post, which was online briefly on September 6, the hackers expressed their surprise at what they called “terrible security practices.” Cybersecurity is important The hackers claimed that, although they had found flaws in […]

The owner of Burger King and Popeyes suffers a cyberattack that describes its security practices as terrible

Restaurant Brands International (RBI), owner of well-known chains such as Burger King, Popeyes, and Tim Hortons, has been the target of a cyber attack that revealed serious vulnerabilities in its IT security. Two hackers, known as BobDaHacker and BobTheShoplifter, published a blog detailing their findings, highlighting their ability to access all RBI establishments and listen to conversations in the drive-thrus. In the post, which was online briefly on September 6, the hackers expressed their surprise at what they called “terrible security practices.”

Cybersecurity is important

The hackers claimed that, although they had found catastrophic security flaws, they did not retain any customer data during their investigation, and assured that they followed responsible disclosure protocols. Their intention, according to them, was to expose security issues to improve the company’s protection. However, the blog post was removed 24 hours after its release, after RBI filed a DMCA complaint, although it can still be accessed through Wayback Machine.

Despite the seriousness of the situation, the hackers praised RBI’s response speed in addressing the identified vulnerabilities, although the company has not issued direct comments on the matter. “RBI’s response was impressive,” the attackers noted, reiterating that no customers were harmed during the process.

This incident highlights the need for companies to strengthen their security measures in an environment where cyberattacks are becoming increasingly common. The situation of RBI could serve as a serious reminder of the risks of digital security, and the fact that these vulnerabilities were discovered by hackers for improvement purposes should spark a debate on how companies manage their cyber defenses.

Avast Free Antivirus
Avast Free Antivirus DOWNLOAD
Author SoftonicPosted on September 8, 2025September 8, 2025Categories NewsTags BobDaHacker, BobTheShoplifter, Burger Kings, ciberseguridad, drive-thrus, hackers, Popeyes, prácticas de seguridad terribles, RBI, Restaurant Brands International, Seguridad

If you want to know where all your tech devices are, this Bluetooth tracker is your best solution

The Bluetooth tracker Rolling Square AirCard Pro, which is the size of a credit card, is positioning itself as a standout option in the field of tracking devices. This device allows users to track items such as wallets, phones, pets, and luggage through an app, offering a practical solution for those who often misplace their belongings. A Bluetooth tracker with which you will never lose anything again One of the most notable features of the AirCard Pro is its rechargeable 220 mAh battery, which promises to last up to 12 months with wireless charging. This represents a […]

If you want to know where all your tech devices are, this Bluetooth tracker is your best solution

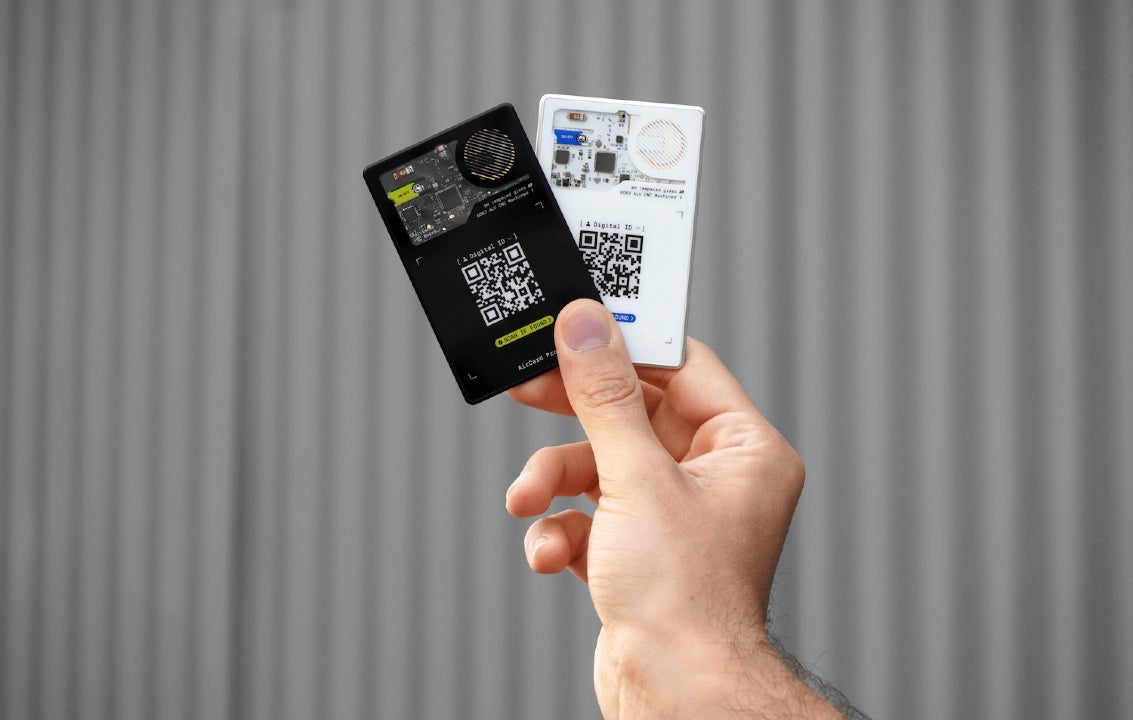
The Rolling Square AirCard Pro Bluetooth tracker, which is the size of a credit card, is positioning itself as a standout option in the field of tracking devices. This device allows users to track items such as wallets, phones, pets, and luggage through an app, providing a practical solution for those who often misplace their belongings.

A Bluetooth tracker that will help you never lose anything again

One of the most notable features of the AirCard Pro is its rechargeable 220 mAh battery, which promises to last up to 12 months with wireless charging. This represents a significant improvement compared to trackers that rely on disposable batteries, eliminating the need for frequent battery changes and providing a more convenient experience.

There are two versions of the AirCard Pro, one specifically designed for the Android Find Hub network and another for Apple’s Find My service. Both versions allow users to track their devices and activate lost mode, ensuring that their important items are not lost.

In terms of design, the AirCard Pro features a CNC-machined aluminum frame and epoxy resin, providing a robust quality and a transparent finish. Additionally, it includes a speaker that emits sounds to help locate lost items. A QR code on the outside functions as a business card, allowing users to share selective information such as their email and phone number.

With a slim design that barely doubles the thickness of a standard credit card, the AirCard Pro can easily fit into any wallet. Its compact structure makes it a versatile solution for those who need to keep constant track of their belongings. Priced at $40, Rolling Square is presenting this device as an attractive option in the personal tracker market.

Apple Store
Apple Store DOWNLOAD
Author SoftonicPosted on August 19, 2025August 19, 2025Categories News, Software>SecurityTags 220AH, AirCrad Pro, Android, Apple, Bluetooth, Seguridad

Microsoft fixes 111 vulnerabilities that exposed your computer to all kinds of threats

Microsoft has released updates to address a total of 111 vulnerabilities in its software portfolio, of which 16 have been classified as critical. Among these are significant flaws such as CVE-2025-53786, which affects hybrid implementations of Microsoft Exchange Server, and CVE-2025-53779, a privilege escalation vulnerability in Windows Kerberos that was publicly disclosed during the announcement. A solution so you don’t have to suffer from unforeseen issues The recently identified BadSuccessor vulnerability allows an attacker who already has access to certain attributes of Active Directory to compromise a domain, although it only affects 0.7% of […]

Microsoft fixes 111 vulnerabilities that exposed your computer to all kinds of threats

Microsoft has released updates to address a total of 111 vulnerabilities in its software portfolio, of which 16 have been classified as critical. Among these are significant flaws such as CVE-2025-53786, which affects hybrid implementations of Microsoft Exchange Server, and CVE-2025-53779, a privilege escalation vulnerability in Windows Kerberos that was publicly disclosed during the announcement.

A solution so you don’t have to suffer from unforeseen events

The BadSuccessor vulnerability, recently identified, allows an attacker who already has access to certain attributes of Active Directory to compromise a domain, although it only affects 0.7% of the domains in circulation. Experts point out that this flaw can enable an attacker, starting from limited administrative rights, to gain full control of the domain, using techniques such as Kerberoasting or Silver Ticket.

In addition, Microsoft has fixed four remote code execution vulnerabilities that allowed attackers to execute arbitrary commands and compromise systems without client intervention. The firm Check Point has revealed a flaw related to a Rust-based component of the Windows kernel that can cause system crashes and has warned that it could pose a significant risk for companies with large or remote templates.

A relevant aspect is the vulnerability CVE-2025-50154, which allows an attacker to extract NTLM hashes without user interaction, even on fully updated systems. This facilitates relay attacks and unauthorized access, raising concerns about security in corporate environments.

The updates not only address existing vulnerabilities, but also strengthen security measures in applications like Azure OpenAI and Microsoft 365 Copilot BizChat, which have already been mitigated without any action required from users.

Windows 11
Windows 11 DOWNLOAD
Author SoftonicPosted on August 13, 2025August 13, 2025Categories News, Windows softwareTags ciberseguridad, Copilot, ejecución remota, OpenAI, Seguridad, software, vulnerabilidad, Windows

Posts pagination

Previous page Page 1 Page 2 Page 3 … Page 5 Next page

Recent Posts

  • Widows Is Now Free on Pluto TV: Steve McQueen’s crime thriller
  • Tesla renames Full Self-Driving in Europe: Assisted Driving appears on EU sites
  • Microsoft updates its AI push with “Super Intelligence”: against OpenAI and Anthropic
  • Microsoft Outlook retires Themes by Copilot this October
  • Over the Garden Wall is back in Prime Video’s Top 10 for Halloween

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025
  • April 2025
  • March 2025
  • February 2025
  • January 2025
  • December 2024
  • November 2024
  • October 2024
  • September 2024
  • August 2024
  • July 2024
  • June 2024
  • May 2024
  • April 2024
  • March 2024
  • February 2024
  • January 2024
  • December 2023
  • November 2023
  • October 2023
  • September 2023
  • August 2023
  • July 2023
  • June 2023
  • May 2023
  • April 2023
  • March 2023
  • February 2023
  • January 2023
  • December 2022
  • November 2022
  • October 2022
  • September 2022
  • August 2022
  • July 2022
  • June 2022
  • May 2022
  • April 2022
  • March 2022
  • February 2022
  • January 2022
  • December 2021
  • November 2021
  • October 2021
  • September 2021
  • August 2021
  • July 2021
  • June 2021
  • May 2021
  • April 2021
  • March 2021
  • February 2021
  • January 2021
  • December 2020
  • November 2020
  • October 2020
  • September 2020
  • August 2020
  • July 2020
  • June 2020
  • May 2020
  • April 2020
  • March 2020
  • February 2020
  • January 2020
  • December 2019
  • November 2019
  • October 2019
  • September 2019
  • August 2019
  • July 2019
  • June 2019
  • May 2019
  • April 2019
  • March 2019
  • February 2019
  • January 2019
  • December 2018
  • November 2018
  • October 2018
  • September 2018
  • August 2018
  • July 2018
  • June 2018
  • May 2018
  • April 2018
  • March 2018
  • February 2018
  • January 2018
  • December 2017
  • November 2017
  • October 2017
  • September 2017
  • August 2017
  • July 2017
  • June 2017
  • May 2017
  • April 2017
  • March 2017
  • February 2017
  • January 2017
  • December 2016
  • November 2016
  • October 2016
  • September 2016
  • August 2016
  • July 2016
  • June 2016
  • May 2016
  • April 2016
  • March 2016
  • February 2016
  • January 2016
  • December 2015
  • November 2015
  • October 2015
  • September 2015
  • August 2015
  • July 2015
  • June 2015
  • May 2015
  • April 2015
  • March 2015
  • February 2015
  • January 2015
  • December 2014
  • November 2014
  • October 2014
  • September 2014
  • August 2014
  • July 2014
  • June 2014
  • May 2014
  • April 2014
  • March 2014
  • February 2014
  • January 2014
  • December 2013
  • November 2013
  • October 2013
  • September 2013
  • August 2013
  • July 2013
  • June 2013
  • May 2013
  • April 2013
  • March 2013
  • February 2013
  • January 2013
  • December 2012
  • November 2012
  • October 2012
  • September 2012
  • August 2012
  • July 2012
  • June 2012
  • May 2012
  • April 2012
  • March 2012
  • February 2012
  • January 2012
  • December 2011
  • November 2011
  • October 2011
  • September 2011
  • August 2011
  • July 2011
  • June 2011
  • May 2011
  • April 2011
  • March 2011
  • February 2011
  • January 2011
  • December 2010
  • November 2010
  • October 2010
  • September 2010
  • August 2010
  • July 2010
  • June 2010
  • May 2010
  • April 2010
  • March 2010
  • February 2010
  • January 2010
  • December 2009
  • November 2009
  • October 2009
  • September 2009
  • August 2009
  • July 2009
  • June 2009
  • May 2009
  • April 2009
  • March 2009
  • February 2009
  • January 2009
  • December 2008
  • November 2008
  • October 2008
  • September 2008
  • August 2008
  • July 2008
  • June 2008
  • May 2008
  • April 2008
  • March 2008
  • February 2008
  • January 2008
  • December 2007
  • November 2007
  • October 2007
  • September 2007
  • August 2007
  • July 2007
  • June 2007
  • May 2007
  • April 2007
  • March 2007
  • February 2007
  • January 2007
  • December 2006
  • November 2006
  • September 2006
  • August 2006
  • June 2006
  • May 2006
  • July 2001
  • January 2001
  • November 2000
  • September 2000
  • August 2000
  • July 2000
  • April 2000
  • March 2000

Categories

  • Affiliate post
  • Expert Review
  • Gaming
  • Guides
  • How to
  • Legacy how To
  • News
  • Noticias
  • Software>Security
  • Sponsored
  • Trucos y Consejos
  • Uncategorized
  • Windows software

Meta

  • Log in
  • Entries feed
  • Comments feed
  • WordPress.org
Softonic English Proudly powered by WordPress